
CBE Issues New Regulations for Credit Guarantee Companies
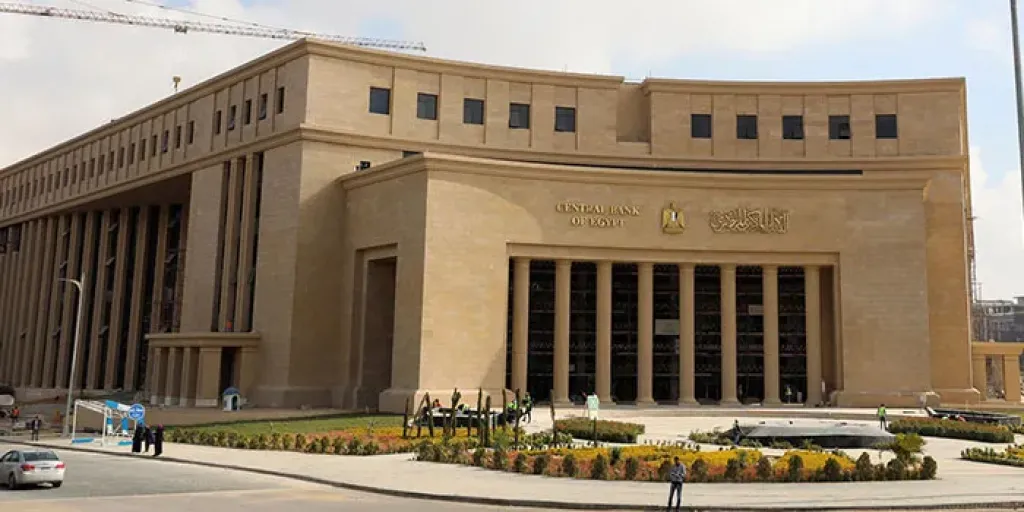
The Board of Directors of the Central Bank of Egypt (CBE) has issued new instructions regarding the licensing, oversight, and supervision of credit guarantee companies, in line with the Central Bank and Banking System Law No. 194 of 2020. These instructions aim to establish an integrated regulatory framework to support the financial soundness, stability, and operational efficiency of credit guarantee companies.
Licensing and Registration Requirements
Under the new rules, credit guarantee companies must be established as Egyptian joint-stock companies with fully nominal shares and a minimum issued and paid-up capital of EGP 50 million. The CBE mandated complete transparency in ownership structures, including identifying ultimate beneficial owners and related parties, verifying the legitimacy of funds, and ensuring compliance with market competition rules without conflicting with public economic interests. Furthermore, founders, beneficial owners, and key executives must demonstrate integrity, sound reputation, financial solvency, and relevant experience.
Governance, Risk Management, and Outsourcing
Companies are required to submit comprehensive financial and economic feasibility studies detailing business objectives, target sectors, risk measurement techniques, and hedging tools. The framework obligates companies to implement clear strategies, effective internal controls, risk management, governance, and outsourcing policies. Companies retain full accountability for services delegated to third-party technology and outsourcing providers. Additionally, qualified entities must be appointed to audit IT infrastructure and information security standards. Companies are also subject to an annual supervisory fee of EGP 100,000 payable every January.
Timeline for Regulatory Compliance
The CBE has granted credit guarantee companies a one-year grace period to adjust their status, extended to two years for compliance with information security, cybersecurity standards, and regulatory ratios. Companies must submit a detailed compliance timeline to the Supervision Sector within three months, identifying existing gaps and targeted corrective actions.
related topics
 Central Bank Sets Data Security Rules for Credit Guarantee Companies
 CBE Sets New Ownership Rules for Credit Guarantee Companies
 Central Bank Sets Governance and Control Rules for Credit Guarantee Companies
 CBE Sets Merger, Split and Key Management Rules for Credit Guarantee Companies
 Central Bank Details License Cancellation and Liquidation Rules for Credit Guarantee Firms
 Credit Guarantee Companies Face EGP 50 Million Capital Requirement
 CBE Rules for Credit Guarantee Companies and New Branches
 Egypt’s Central Bank Issues New Rules for Credit Guarantee Companies
 Sahl App Launches Direct Natural Gas Bill Payments and Prepaid Meter Card...
 myFawry App Transactions Surge 68.5% to EGP 48 Billion in H1 2026...
 Mastercard collaborates with AFS to launch corporate credit and prepaid cards in...
 valU Prepaid Card activation, MENA FinTech spending rails, Consumer liquidity solutions Egypt,...