iScore Strengthens Data Security Framework With SOC 2 Type II and ISO IT Service Certification
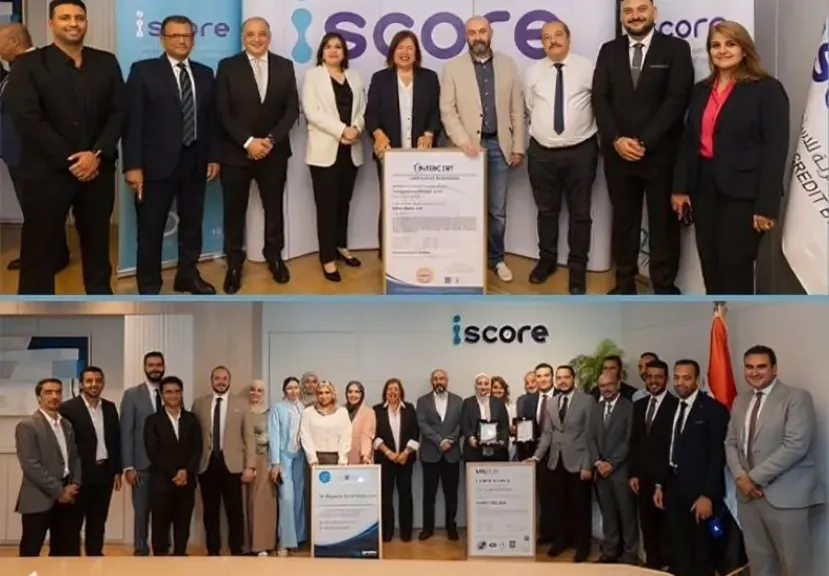
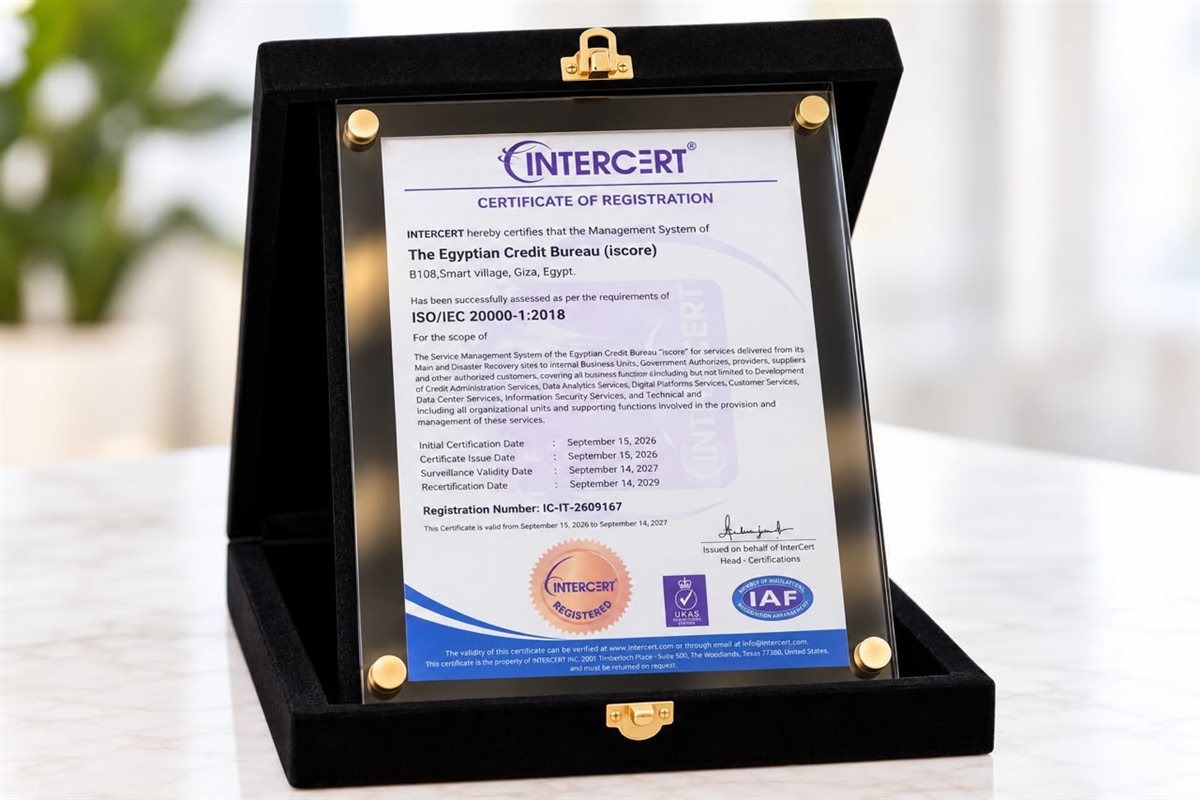
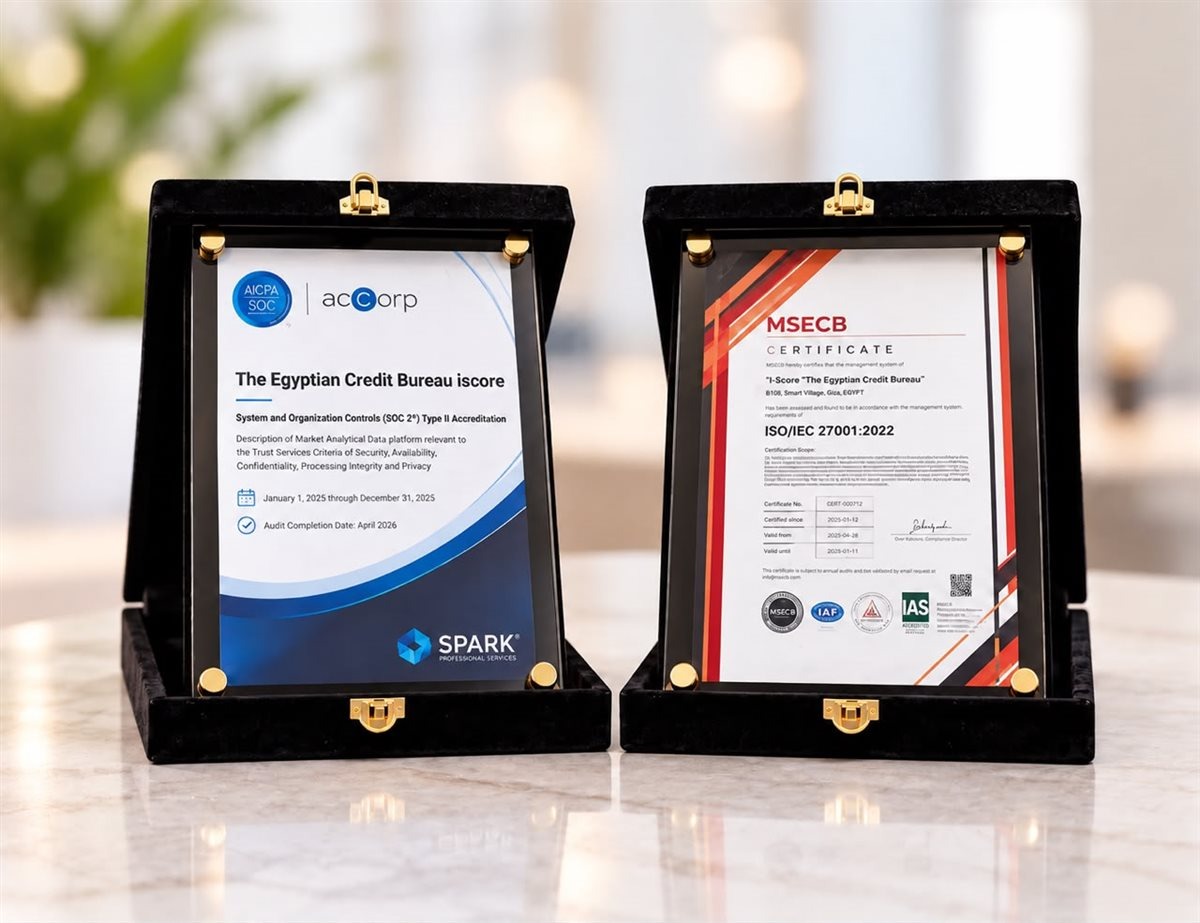
The Egyptian Credit Bureau, iScore, has expanded its international technology and security certifications, securing SOC 2 Type II and ISO/IEC 20000-1:2018 while renewing its ISO 27001 certification for information security management.
The combination strengthens the governance framework surrounding one of Egypt’s most sensitive financial data infrastructures, covering not only how information is protected but also how technology services and operational controls are managed over time.
For a credit bureau, the distinction is important. Security certification alone addresses how an organization establishes and maintains an information security management system, while SOC 2 Type II goes further by assessing whether relevant controls operated effectively over a defined period.
Adding ISO/IEC 20000-1:2018 brings IT service management into the same framework.
SOC 2 Type II Goes Beyond Security Policies
Among the new certifications, SOC 2 Type II provides an important additional layer of assurance.
Unlike assessments focused largely on whether controls have been appropriately designed at a particular point in time, a Type II report evaluates their operating effectiveness over a specified period.
For iScore, this provides independent assurance around the effectiveness and continuity of security and operational controls supporting its technology environment.
That is particularly relevant to a business whose core operations depend on receiving, processing and managing financial and credit information.
ISO 27001 Renewal Keeps Information Security at the Core
iScore has also renewed its ISO 27001 certification, maintaining the international standard covering information security management systems.
The certification provides a structured framework for identifying information-security risks, implementing controls and continually managing those risks.
For organizations operating within financial infrastructure, maintaining that framework is increasingly important as the volume of digital transactions, interconnected financial services and data exchange continues to grow.
The renewal indicates that iScore is maintaining its information-security management framework rather than treating certification as a one-time exercise.
IT Service Management Added to the Certification Framework
The company has also obtained ISO/IEC 20000-1:2018, an international standard focused specifically on IT service management.
The certification covers the systems and processes used to plan, deliver, monitor and continually improve technology services.
For iScore, it connects cybersecurity and data protection with another critical requirement: ensuring that the technology services supporting credit information remain reliable and efficiently managed.
The company said the framework supports business continuity, service quality and operational efficiency while maintaining information-security and data-protection requirements.
Credit Infrastructure Makes Data Governance Critical
iScore occupies a distinctive position within Egypt’s financial ecosystem because its services sit behind credit decisions made across the market.
Credit bureaus aggregate and process information used by financial institutions to assess customers and manage credit risk, making the integrity, availability and protection of their technology systems especially important.
As financial services become increasingly digital, the infrastructure supporting credit assessment must also manage growing requirements around cybersecurity, service availability and data governance.
By combining ISO 27001, SOC 2 Type II and ISO/IEC 20000-1:2018, iScore is effectively extending its assurance framework from protecting information to demonstrating that security controls operate continuously and that the technology services surrounding that data are managed under internationally recognized standards.